GDPR for Websites: Your Obligations for Cookies, Forms and Legal Notices
GDPR for websites: sort your cookies, set up a banner you can maintain, limit your forms and write your legal pages. A step-by-step action plan by priority.
GDPR for websites: which obligations should you tackle first?
A website that processes personal data must inform visitors, obtain their consent before setting any non-essential tracker, limit collection to what is necessary, publish legal notices and a privacy policy, and make it possible for people to exercise their rights. These are the basics of GDPR compliance for a website.
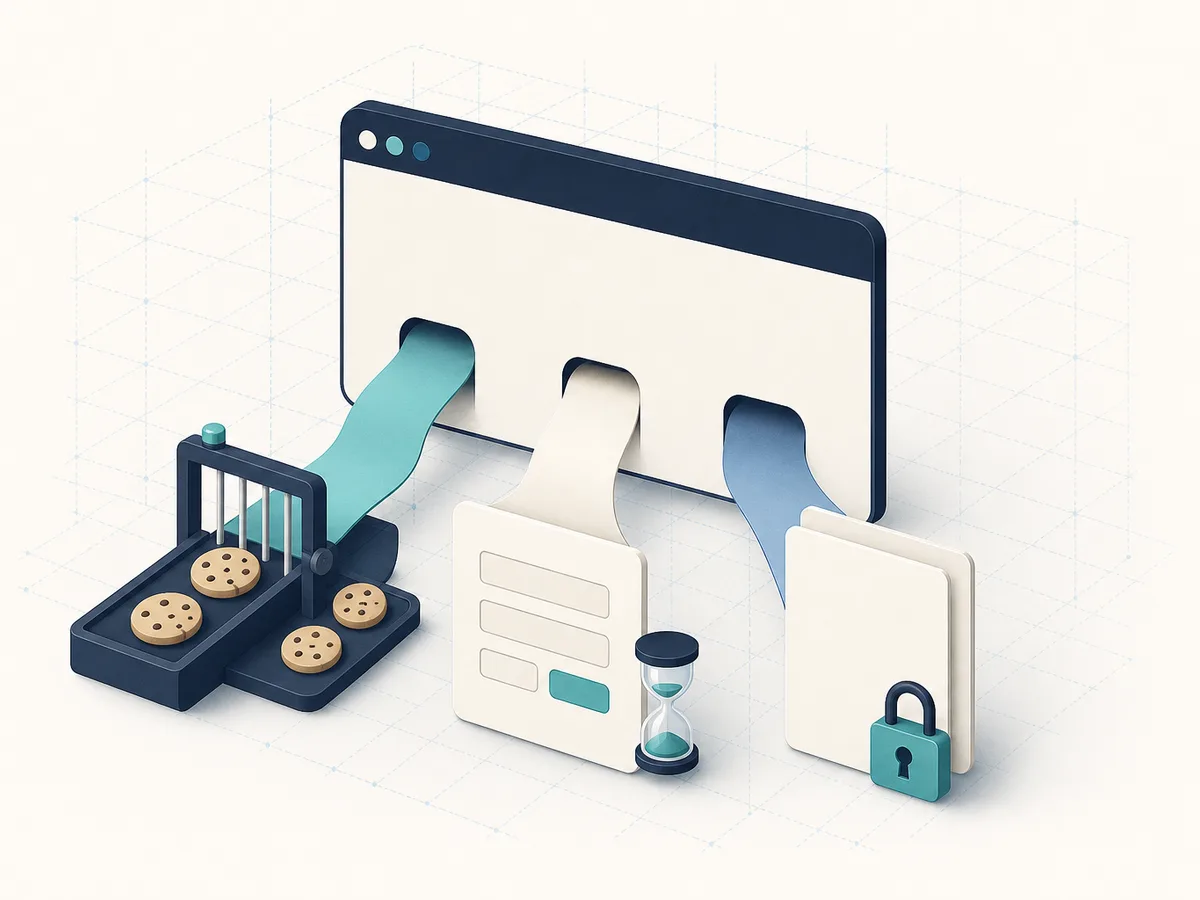
In practice, the work breaks down into three workstreams:
- Cookies: sort your trackers, block those that require consent and collect a valid choice.
- Forms: ask only for the fields you need, display the purpose and set a retention period.
- Legal pages: write clear legal notices and a clear privacy policy, and keep them up to date.
For a business website, the GDPR mostly changes the way you work. Compliance becomes a design requirement, not a last-minute add-on. It affects the code, third-party tools and internal processes.
Tackle it step by step, starting with the most visible risks.
Cookies: consent, exempt trackers and trackers that require consent
Not all cookies are treated the same way. They are sorted by purpose.
Exempt from consent
Trackers that are strictly necessary for the service do not require prior consent: login sessions, e-commerce carts, security, and storing the consent choice. They must still be listed in the privacy policy.
Subject to consent
These require consent before anything is set:
- advertising cookies;
- social network trackers (share buttons, pixels);
- audience measurement, unless it is configured to qualify for the CNIL exemption, which must be checked tool by tool.
Valid consent
Consent must be freely given, informed and unambiguous. No pre-ticked boxes, no hidden refusal option. Users know what they are accepting and why. They can also withdraw their choice as easily as they gave it.
Setting up a cookie banner you can maintain
A reliable cookie banner rests on four implementation rules:
- Prior blocking: no analytics, advertising or social network script loads before consent is given.
- Equal refusal: "Reject all" is as visible as "Accept all".
- Proof: you keep the choice, its date and the banner version.
- Permanent access: a link in the footer lets users change their choice.
As for the trade-off, a consent management platform deploys quickly and keeps up with regulatory changes. A custom build adapts better to a specific product, but requires maintenance.
Be aware: without consent, audience measurement becomes partial.
Forms: collect only the data you need
A contact form doesn't need to know everything about your visitor. Apply data minimisation: every field must serve a specific purpose.
First things to remove:
- phone number, if you reply by email;
- title, company or job role, if they don't change your reply;
- "How did you hear about us?", to be replaced by audience measurement.
A shorter form is quicker to fill in. Test conversion before and after to measure the effect.
Around the submit button:
- display the purpose: "This data is used only to respond to your request";
- add an unticked checkbox only if you pursue another purpose, such as a newsletter;
- set a retention period and purge the data automatically;
- send data over HTTPS, with access to received messages restricted.
Legal notices and privacy policy: what should they contain?
These two pages do not serve the same purpose. Write them separately.
Legal notices
They identify who is behind the site:
- the publisher: company name or name, address, contact details, legal form, share capital, registration number;
- the publication director;
- the host: name, address and phone number.
Privacy policy
It explains what happens to the data:
- the data controller and their contact details;
- the purposes, each with its legal basis;
- the recipients, including processors;
- retention periods;
- individuals' rights and how to exercise them.
Write in plain sentences, without unnecessary legal jargon. Update both pages whenever you add a new tool, form or provider.
Individuals' rights, processors and security: the points most often overlooked
A site that looks compliant on the surface can still be fragile if the organisation behind it doesn't keep up.
- Individuals' rights: define who receives a request for access, rectification or erasure, where to look for the data and how quickly to respond.
- Processors: list your host, emailing tool and analytics provider, then check each one's data processing agreement.
- Security: HTTPS, restricted access, backups.
A website can't do everything. Internal processes and legal advice are still necessary.
Where to start: auditing and prioritising the work
Start with a compliance audit, in four short steps.
- Map: list the data collected, where it comes from, where it goes and which third-party tools are involved.
- Audit: test the cookies set before any choice is made, then review each form.
- Fix: deal first with the most visible risks, such as trackers running without consent.
- Document: record your decisions and updates.
Some points require legal advice, notably legal bases. A technical partner implements the changes but doesn't replace a lawyer.